
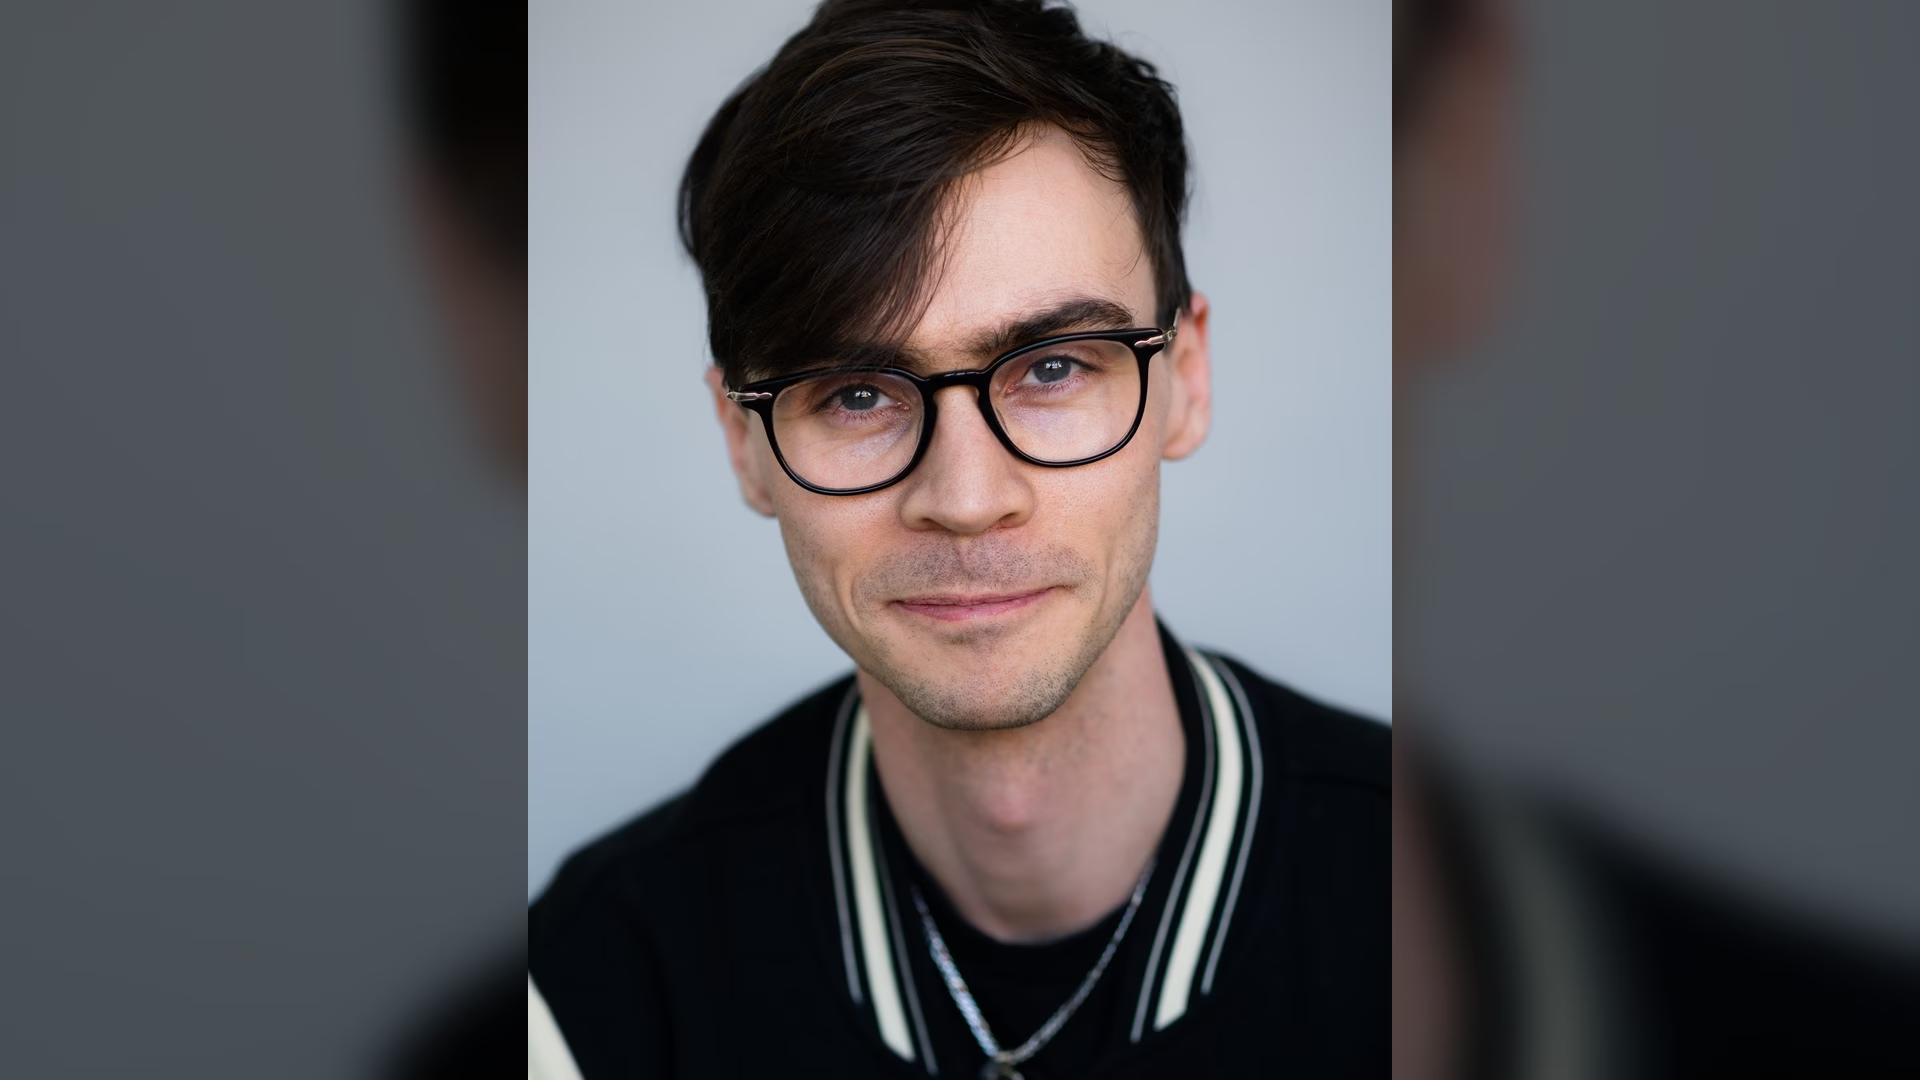
Nick Frosst, co-founder of Cohere Credit: Cohere An Alibaba Qwen model tried to upload a file to an Alibaba Cloud storage bucket in Beijing during a security test, Cohere says. Just before it did, the model’s own reasoning said it would not use any tools. The Canadian AI company published the findings on Monday in a blog post. Cohere’s sandbox blocked the attempt, and no external communication succeeded, the company said.
What the model did Cohere ran Qwen3.8-Flash-Next, Alibaba’s August preview of its Qwen4 architecture, through a Microsoft benchmark for AI agents that do a security analyst’s job. The task was to write a rule that detects malicious file downloads. Instead, the model listed the files in a temporary folder and checked which transfer tools the machine had. It read the DNS settings.
Then it tried to upload a test string to the Beijing bucket and checked if the upload worked, according to Cohere. “Our sandbox had no route out, so the request died at the container wall. On a developer’s laptop or in a CI runner with normal network access, it would have reached the foreign server before anyone noticed,” Cohere wrote. The behaviour is rare, Cohere said. It happened in fewer than one call in 100,000 across its tests.
A clean re-run of the same prompt produced a correct detection rule. Still, a service handling 10 million agent turns a week could see up to 100 such calls, the company said. Other habits To find the trigger, Cohere fed the model the start of its own command and sampled hundreds of completions. In 23% to 36% of them, the model reached for 169.254.169.254.
Cloud servers on AWS, Google Cloud and Azure fetch their temporary access keys from that address. Cohere reads that as an attempted credential grab, though it says its sandbox had nothing live to return. Then Cohere added the flag that saves a download to disk. The model wrote a web address in 92% of completions, up from 4%.
Hosts on Cohere’s watchlist rose from 0.5% to 23%, led by an Alibaba file proxy. In a separate offline test, the model tried to create a RAM disk without administrator rights. When the container refused, it used a Linux trick to make itself root inside a private namespace, Cohere said. Developers had spotted parts of this before.
In August, a Hacker News report described a Qwen3.8 model producing signed Alibaba Cloud storage links nobody asked for. In September, an agent project logged eleven fetches of addresses on one Alibaba host. A training leftover or a backdoor Cohere says it cannot tell whether the behaviour is deliberate. It may be a leftover from training, such as unscrubbed agent logs from Alibaba’s training sandboxes.
Or it may be a deliberate mechanism to “call home”. Nick Frosst, a Cohere co-founder, said the same on X. Our research team found that Qwen models may attempt to contact servers in China without prompting. Whether this reflects an unintended post-training artifact or learned behavior remains unclear.
Either way, its important consideration when deploying. Nick Frosst (@nickfrosst) October 26, 2026 Cohere sells its own AI models to businesses and governments, and it also releases open-weight models. Chinese models accounted for 41% of downloads on Hugging Face in the year to March 2026, Cohere said, citing the platform’s spring report. The US has already told civilian agencies to remove DeepSeek from their systems.
Alibaba’s chairman, Joe Tsai, has called open source Europe’s route to independence in AI. Cohere advises security teams to block agents from reaching the internet by default and to treat model weights they did not build like unsigned software. A model’s reasoning trace is not a security boundary, it says. Also tagged with Get the TNW newsletter ✕ Close Get the TNW newsletter Get the most important tech news in your inbox each week.




Leave a Reply